
Appearance
Project status
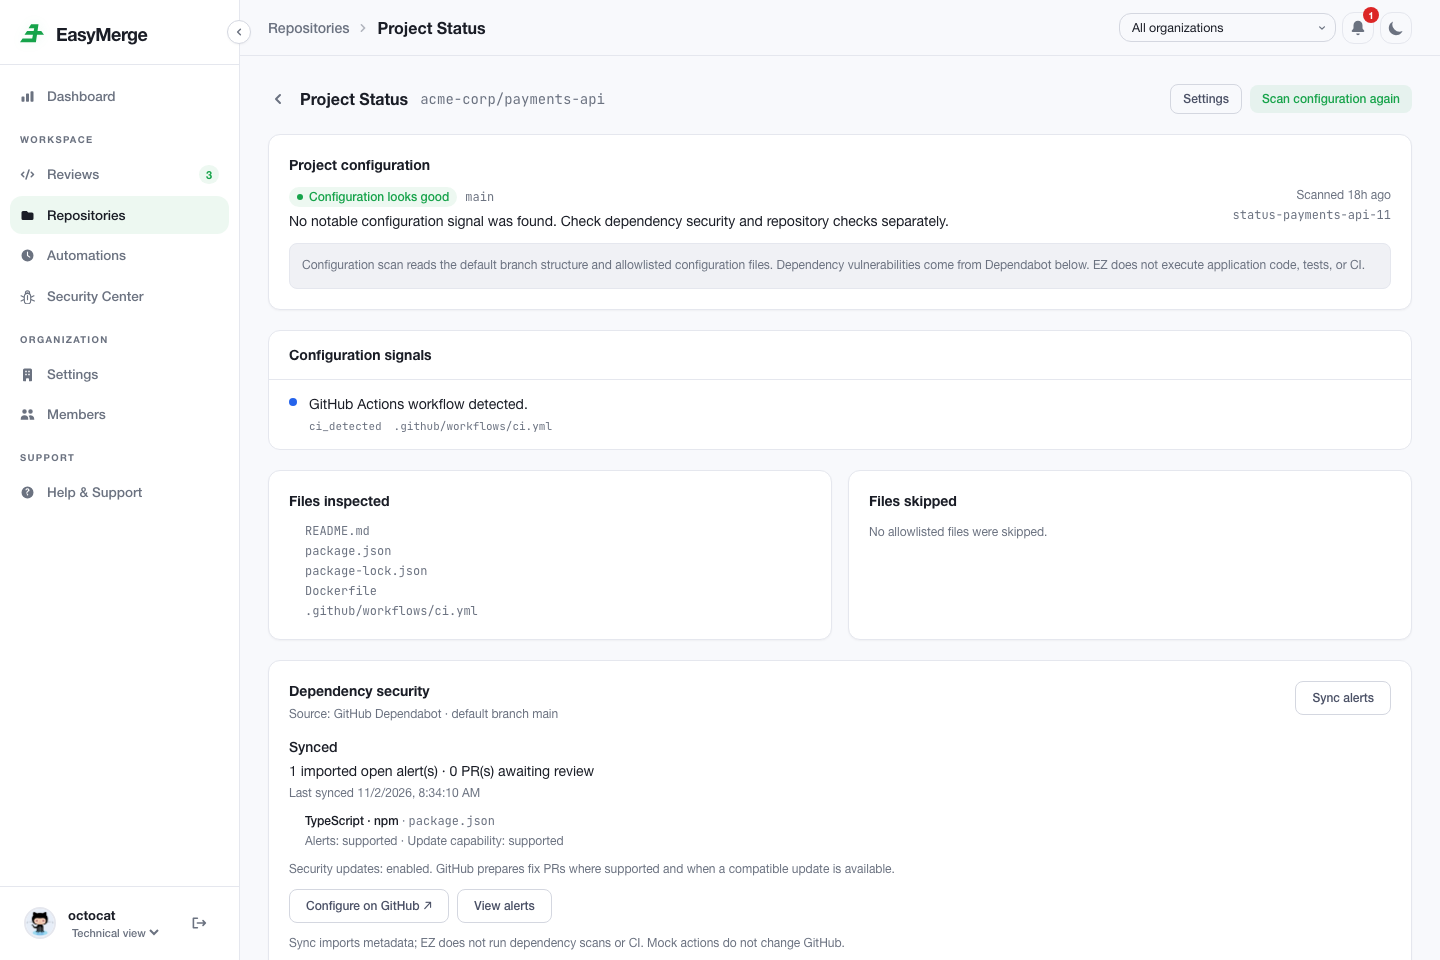
Project status brings together three independent views of a repository's GitHub default branch:
- Project configuration checks how the project is set up without reading application source.
- Dependency security summarises Dependabot setup and alerts.
- Repository checks shows checks reported by the repository's own tooling.
One source can fail without hiding the others, and a good configuration result does not mean its checks passed.
Three ways in:
- the Repositories page;
- a repository's settings page → Project status → View status;
- in Decision view, the project list on the dashboard home.
The page header shows the repository, its default branch and the commit the latest configuration scan read.
Summary cards
When more than one source is available, a row of cards at the top sums each one up: Configuration, Dependency security and Repository checks. Each card shows the current state, a short detail (such as files inspected, open alerts or failing checks) and how fresh the data is, for example Scanned 2h ago or Synced 8h ago. Select a card to jump to its panel.
The cards summarise the panels below them; they are not a combined verdict on the project.
Project configuration
Select Scan configuration the first time or Scan configuration again afterwards. You can also create a Pro automation to run this scan daily or weekly.
The button is disabled while a scan runs. It is also disabled while the repository's EasyMerge installation is suspended; hover over it to see who suspended it and how to have it reactivated. When the default branch has moved on since the last scan, the result reads Needs update.
What the statuses mean
| Status | Meaning |
|---|---|
| Configuration looks good | No notable configuration signal was found within the scan scope |
| Needs attention | The scan found a signal worth reviewing |
| Not enough information | Part of the scan could not be completed |
| Needs update | The default branch changed or the result is more than seven days old |
| Not scanned | No configuration scan has completed yet |
| Scanning… | A scan is running |
| Scan failed | The latest scan did not complete |
What the scan reads
The repository's file and folder structure, plus the contents of a fixed set of files matched by name:
| Kind | Examples |
|---|---|
| Documentation | README and its common text variants |
| Dependency manifests | package.json, composer.json, pyproject.toml, Pipfile, setup.cfg, requirements*.txt, go.mod, pom.xml, build.gradle(.kts), settings.gradle(.kts), packages.config, Directory.Packages.props, *.csproj / *.fsproj / *.vbproj, Cargo.toml, Gemfile, pubspec.yaml |
| Lockfiles | package-lock.json, npm-shrinkwrap.json, pnpm-lock.yaml, yarn.lock, composer.lock, poetry.lock, Pipfile.lock, go.sum, gradle.lockfile, packages.lock.json, Cargo.lock, Gemfile.lock, pubspec.lock |
| Test configuration | vitest.config.*, jest.config.*, playwright.config.*, cypress.config.*, karma.conf.*, .mocharc*, pytest.ini, tox.ini, phpunit.xml(.dist), .rspec |
| Tooling configuration | tsconfig*.json, ESLint config, vite.config.*, analysis_options.yaml |
| CI workflows | .github/workflows/*.yml, .gitlab-ci.yml, .circleci/config.yml, azure-pipelines.yml, bitbucket-pipelines.yml, .travis.yml, Jenkinsfile |
| Deployment | Dockerfile, docker-compose.*, vercel.json, netlify.toml, fly.toml, render.yaml, Procfile, wrangler.*, serverless.*, app.yaml, cloudbuild.yaml, Kubernetes and Helm manifests |
Everything else is left alone: your application source is never read, nor are node_modules, dist, build, vendor or .git. Files that look like secrets (.env, .pem, .key, .p12, id_rsa) are never fetched; a committed .env is flagged from the file listing only.
Files inspected groups the files the scan read by folder, with a count for each. The scan has file count and size limits, and Files skipped gives the reason for any file left out. An incomplete scan reads Not enough information unless it found a more serious signal.
See Data and privacy for what is stored afterwards.
Configuration signals
What EasyMerge found, inside the Project configuration panel, lists what the scan noticed. Most entries are informational, such as whether tests or CI are configured. Only a committed secrets file raises Needs attention; use Copy fix prompt for it. Manifests and lockfiles are read to recognise the project, not to look up vulnerabilities: dependency risks come from Dependabot in the Dependency security panel. Missing test or CI detection uses Copy review prompt, because the scan may not recognise every setup.
Compiler and linter configuration does not count as automated tests.
When a scan fails
The page keeps the last successful result and marks it as an older snapshot. If the scan fails with No supported project files were found on this branch, add a supported file and scan again. Other failures are usually temporary; try again, and report a problem if it repeats.
Dependency security
This panel shows whether GitHub Dependabot is ready, when its metadata last synced, the open-alert count, fix pull requests waiting for review and detected package-manager coverage.
Monitored manifests lists the dependency files GitHub watches, grouped by language and package manager. Expand a group to see whether alerts and security updates are supported for each file.
Use Sync alerts to refresh or View alerts to open the repository in Security Center. For Setup required, Access required or a permissions banner, see Set up GitHub. Configure on GitHub appears only for GitHub repository admins, because GitHub opens a repository's security settings to them alone; everyone else sees Only repository admins can change these settings on GitHub.
While the installation is suspended, Sync alerts is replaced by Sync is paused while this installation is suspended. The last synced data stays visible.
The dependency panel is independent of the configuration scan. Scanning configuration does not start Dependabot or read its alerts.
Plan required
Dependency security and repository checks both come with Security Center. If the repository's organization is on a plan without it, Project Status shows a single line in place of both panels; organization admins can follow View plans from there, and other members are asked to contact an admin. The configuration scan stays available.
Repository checks
Repository checks come from GitHub and your own CI tooling. The panel shows each reported check and the commit it ran against.
No checks reported means GitHub returned none. Checks unavailable means EasyMerge could not read them, which is not the same as having no CI.
EasyMerge reads up to 1,000 check runs and up to 1,000 commit statuses for a commit. If a commit has more of either, the panel shows Checks unavailable rather than a partial list that could look complete.
What project status is not
Project status is not a security audit and does not prove an application is defect-free. It does not affect pull request reviews or post anything to GitHub.